Trust Is Part of the Architecture.
High-stakes assessment requires security, privacy, traceability and operational reliability by design. Here's how DigiAssess approaches each, in plain language for academic leaders and with detail for IT and security teams.
A SOC 2 Type II report is an independent auditor's evaluation of how security controls are designed and how they operated over a period of time.
Request the current report and scope →Security at Every Layer.
Six layers of control, from who can sign in to how the service stays available. Open any layer for the detail your security team will ask about.
Identity & authenticationConfirm who is signing in, staff and candidates alike.
- Authentication for staff and candidates
- Multi-factor authentication, where enabled
- Enterprise identity provider integration, where approved
- Candidate identity verification for assessments
- Face recognition, including offline, where configured
Role-based accessPermissions tied to institutional responsibility.
- Roles for authors, reviewers, evaluators and administrators
- Permissions scoped to programs, courses and assessments
- Approval steps before content is published or results released
- Access governance owned by the institution
Data protectionProtected handling of assessment content and responses.
- Encryption in transit and at rest
- Institutional data segregation
- Controls for biometric and proctoring data
- Responses protected on device during offline delivery
- Controlled synchronization when connectivity returns
- Secure access to item banks
Detail is in the DigiAssess Data Security Statement.
Audit & traceabilityA record of significant actions and decisions.
- Audit trail of significant administrative and assessment actions
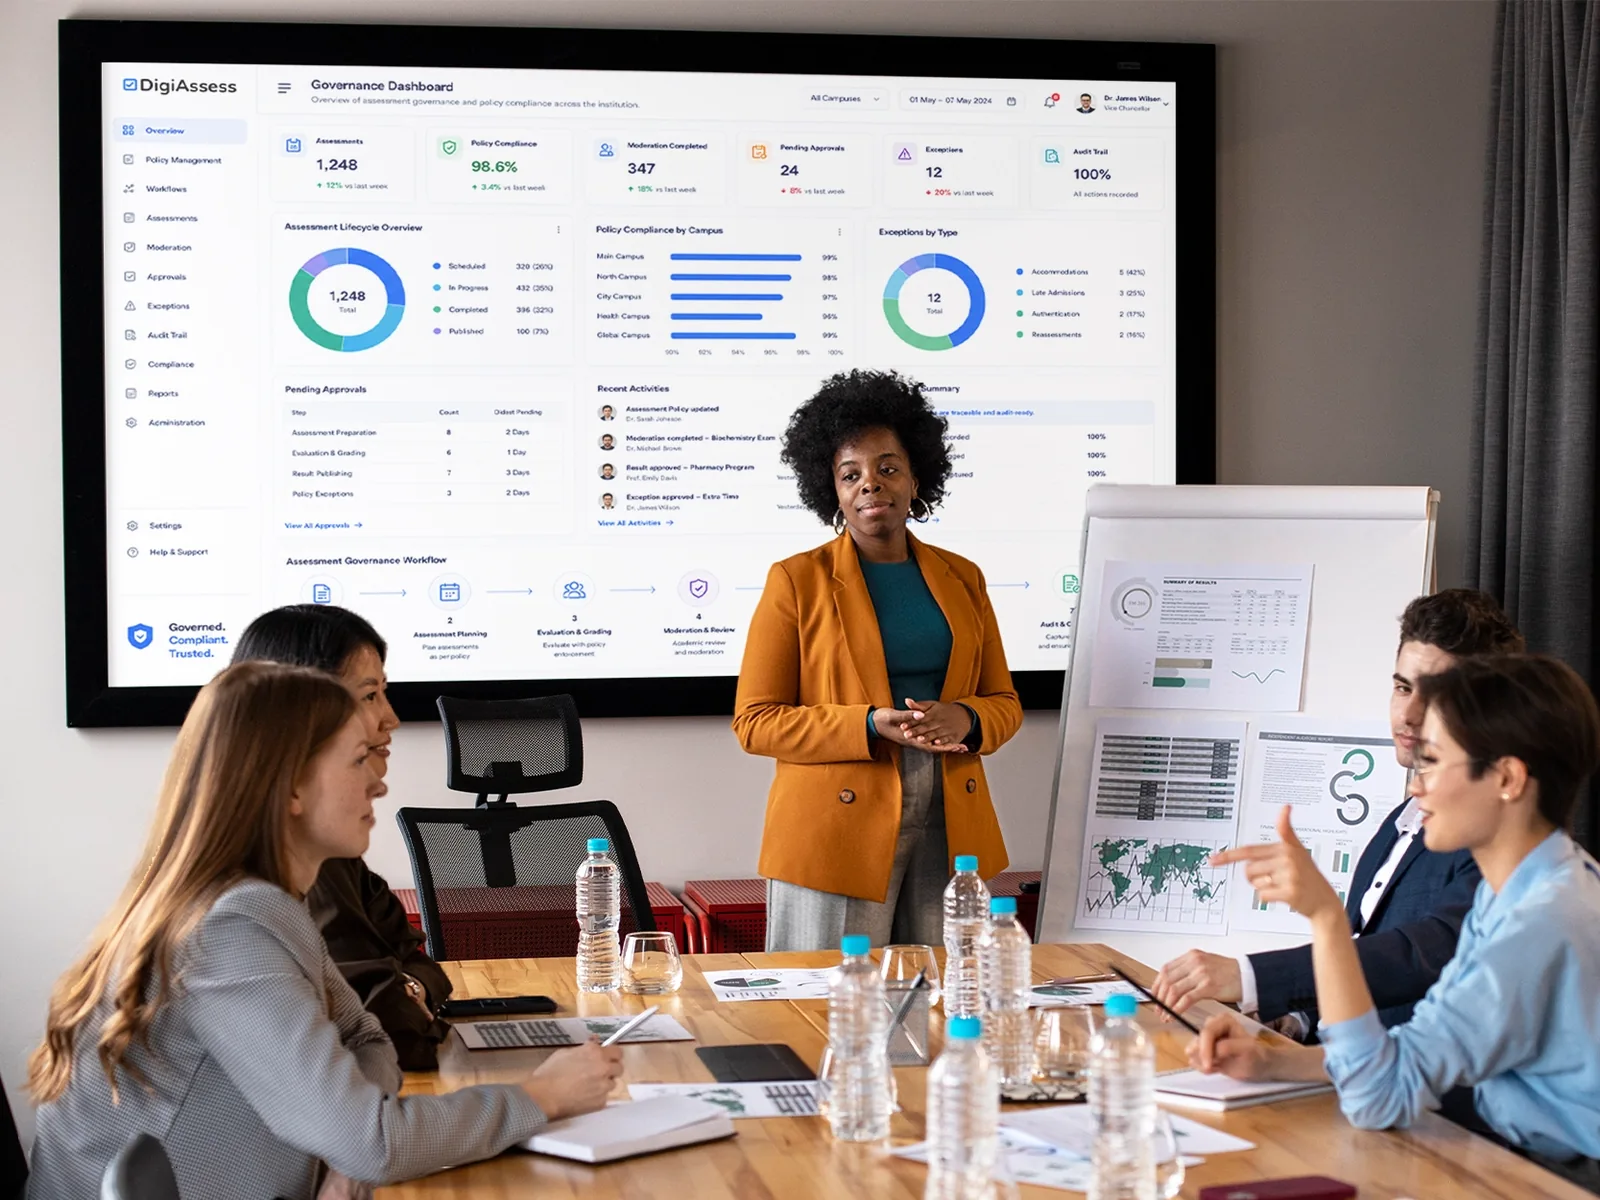
- Traceable approvals, moderation and result workflows
- Session records for monitored assessments
- Authorized interventions recorded with reason and approver
Monitoring & vulnerability managementOperational oversight of the service.
- Monitoring, logging and threat detection
- Network security and traffic controls
- Vulnerability assessment and remediation, with a public vulnerability disclosure policy
- Controls evaluated as part of SOC 2 Type II assurance
Continuity & resilienceAssessments that keep running when conditions change.
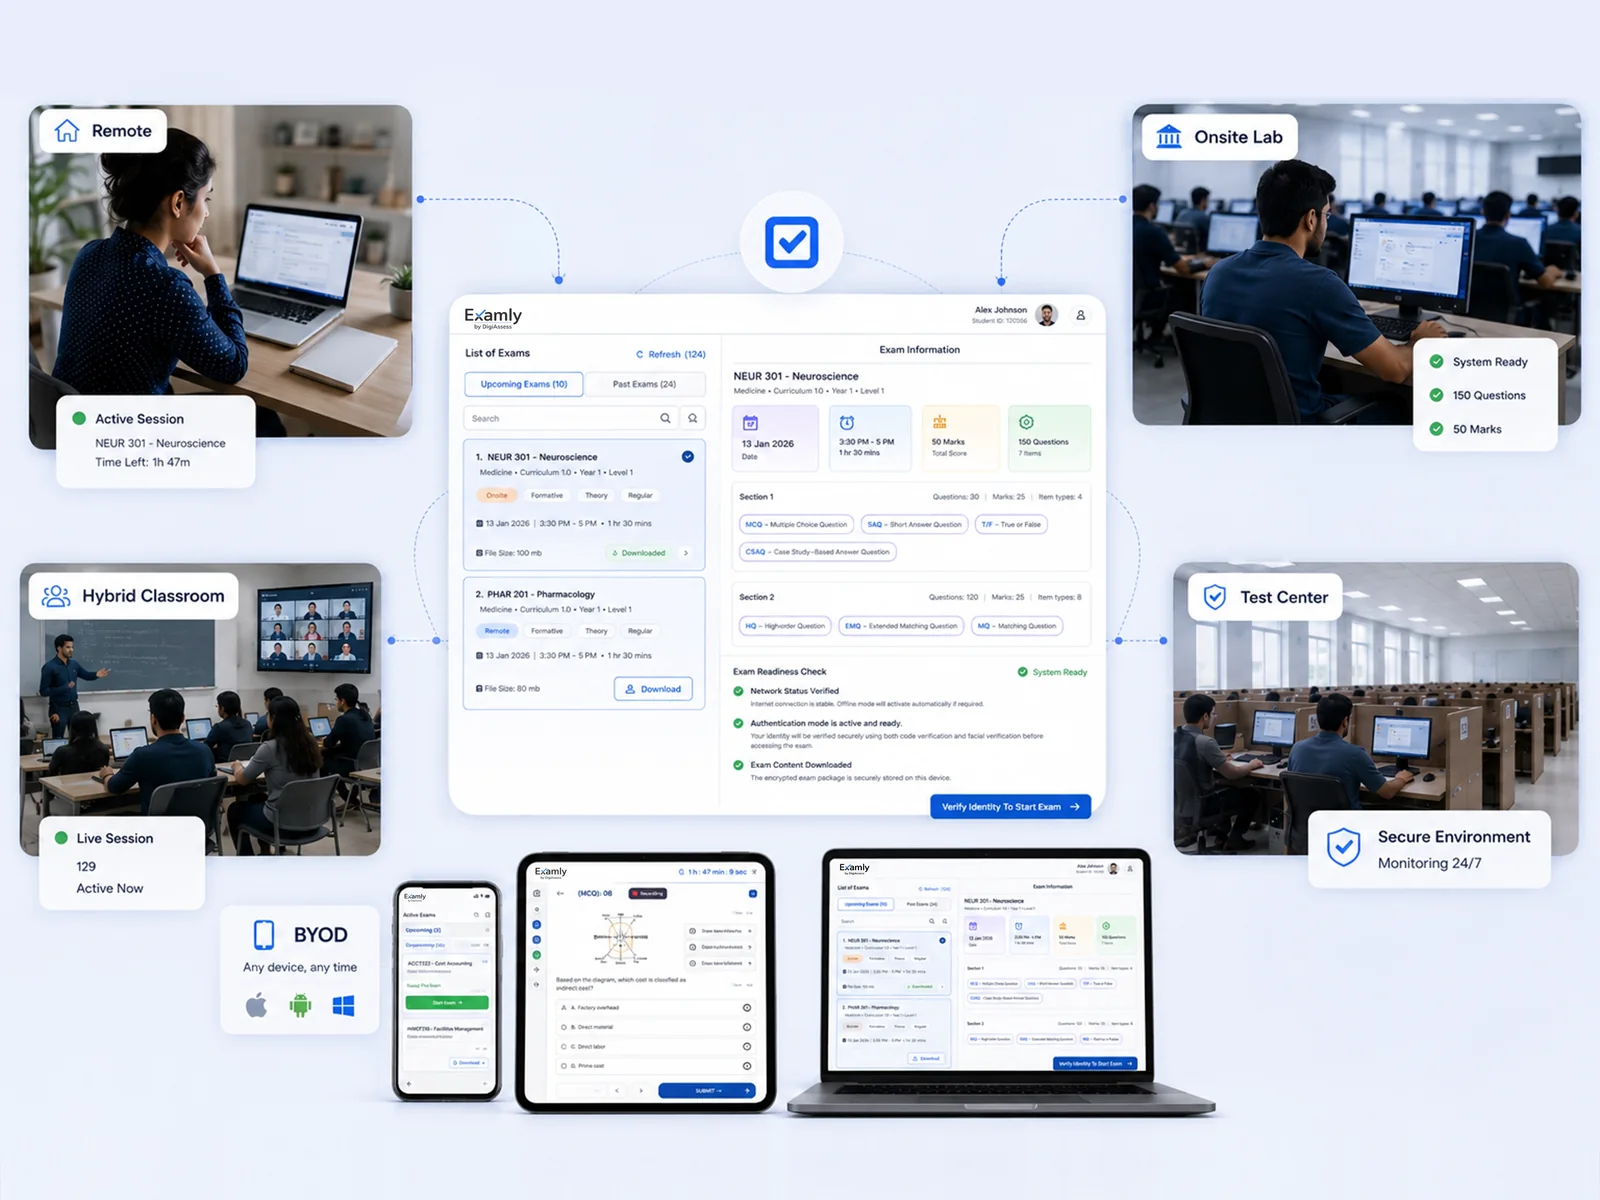
- Offline delivery that doesn't depend on continuous connectivity
- Auto-save and response protection
- Backup and recovery procedures
- Engineered for peak concurrency: load balancing, high availability and failover
- Live operational visibility and exception handling
- See how offline continuity works
Security Continues After Go-Live.
Platform security isn't a one-time configuration. Vulnerabilities, incidents and infrastructure risks change, and the practices behind the platform keep pace.
- Build securelySecure development and testing
- MonitorLogging and operational monitoring
- DetectThreat detection and vulnerability assessment
- RespondIncident investigation and containment
- RecoverBackup and recovery procedures
- ImproveContinuous security improvement
Institutions are notified of incidents according to applicable obligations.
Fit the Deployment to Your Data and Infrastructure Strategy.
Institutions differ in cloud policy, data residency and operating responsibility. DigiAssess is cloud-agnostic, with three operating models.
Institutional SaaS
The fastest route. DigiAssess runs and manages the platform on a subscription basis, with your institution's data segregated from others.
Private SaaS
A dedicated instance for your institution, still operated by DigiAssess, for organizations that need stronger isolation.
Bring your own cloud
Run DigiAssess in a cloud environment your institution controls, to meet regional data-residency requirements.
Responsibilities shown are indicative. They're agreed per contract.
Privacy Without Ambiguity.
Software alone doesn't make an institution compliant with FERPA, GDPR or any other regulation. Security and compliance work on a shared-responsibility model. Here's what DigiAssess provides and what remains with the institution.
Your institution Owns
- Decides what assessment data is collected and why.
- Manages user access and permissions, and approves roles.
- Protects credentials and uses devices and networks securely.
- Sets retention and records policies.
- Provides notices to learners and handles their requests.
DigiAssess Supports
- Secures the platform's infrastructure and application.
- Role-based access controls that enforce your access decisions.
- Security controls independently assessed under SOC 2 Type II.
- Audit trails that show who did what, and when.
- Documented data processing and configurable governance, where supported.
Contractual and data-processing terms are agreed with each institution. Read the Privacy Policy and Data Security Statement, or contact us for data-processing information.
Open to Your Ecosystem. Governed by Design.
Connected systems need governed data flow. DigiAssess connects to your LMS, SIS, ERP, identity provider and quality systems without treating integration as unrestricted access.
- Authenticated
- Role-mapped
- Traceable
- Institution-owned data
Webhooks, message queues and streaming for low-latency, bi-directional changes in high-volume environments.
REST or GraphQL integrations synchronized hourly, nightly or on a custom schedule.
Controlled read-only access with incremental reads, transformed into a unified schema.
Discuss Your Security Requirements.
Procurement or security review underway? Tell us what you need: the SOC 2 Type II report, a security questionnaire or an architecture conversation.